This is an area of great curiosity for me as I was recently appointed as an Advisory Board Member to Xcigence, an industry sector outside of my personal experience sweet spot.
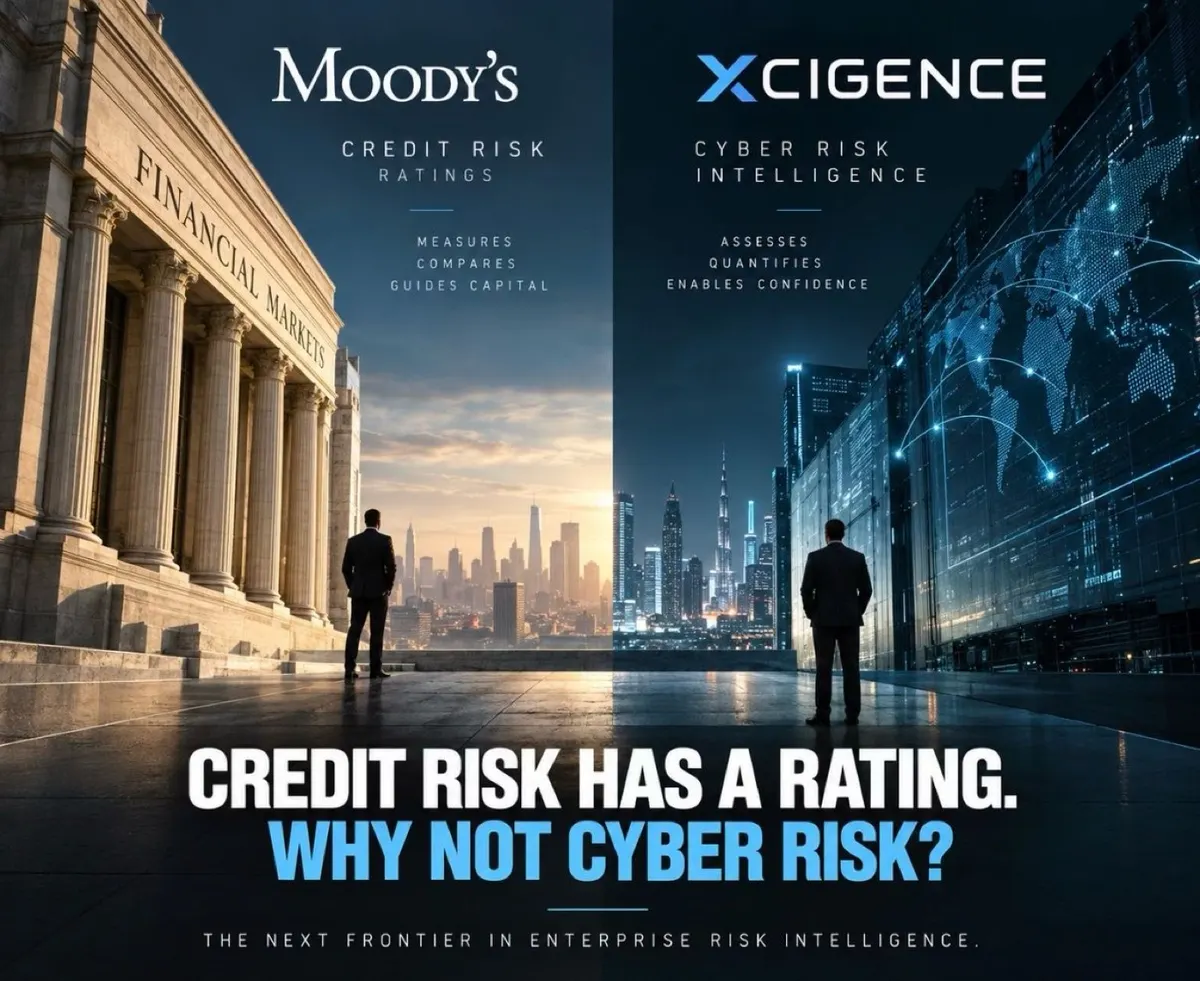
In summary, Moody’s helped make credit risk measurable. Who will do the same for cyber risk?
For decades, financial markets have relied on credit ratings to help answer one fundamental question centered around ‘How much risk are we taking?’
The biggest opportunity in cybersecurity is not another security product. It is making cyber risk impossible to ignore, and easier to understand.
Enterprises, investors and lenders have built entire decision-making systems around that principle.
Yet today, one of the greatest threats to enterprise value is not necessarily financial.
It is digital.
A cyber incident can destroy value, interrupt operations, undermine reputation and erode investor confidence.
And yet, how consistently can we measure, compare and communicate that exposure?
This is what makes the ambition behind Xcigence so compelling. The opportunity is not simply to identify cybersecurity vulnerabilities, it is to help translate cyber exposure into meaningful, decision-ready risk intelligence.
Just as credit ratings brought a common language to financial risk, the next frontier is creating greater clarity around cyber risk.
Cybersecurity is no longer simply an IT conversation. It is a boardroom, investment and an enterprise value conversation.
The biggest opportunity in cybersecurity is not another security product. It is making cyber risk impossible to ignore, and easier to understand.